HomeCategory

Artikuj - E-Privacy Company

GDPR Compliance for SaaS Companies – Practical Privacy Framework

SaaS businesses routinely process information that can fall within the scope of the General Data Protection Regulation (GDPR): account details, business email addresses, IP addresses, support conversations, authentication logs, billing information, usage analytics, and sometimes far more sensitive categories of personal data. This makes privacy governance an operational issue, not simply a privacy-policy exercise. GDPR...
Outsourced Data Protection Officer – Practical GDPR Governance

Privacy responsibilities can quickly become fragmented when personal data is handled across HR, marketing, IT, sales, security, product teams, and external vendors. Someone may maintain privacy notices, another person handles data subject requests, and IT manages security controls, yet nobody has a complete overview of how those activities fit together. An Outsourced Data Protection Officer...

External DPO Service Switzerland – Practical Privacy Governance

Managing privacy obligations can become difficult when an organization processes personal data across multiple departments, systems, vendors, and jurisdictions. Legal, IT, HR, marketing, security, and management teams may all make decisions affecting personal data, yet few organizations have enough internal privacy expertise to continuously coordinate those activities. An External DPO Service Switzerland provides organizations with...

nFADP Compliance for Companies

Swiss data protection compliance is no longer something companies can treat as a one-time legal documentation exercise. The revised Federal Act on Data Protection (FADP), often referred to as the nFADP, requires organizations to understand what personal data they process, why they process it, where it goes, how it is protected, and what risks that...

Swiss nFADP Compliance Consulting

Swiss organizations and international companies handling personal data connected to Switzerland face a practical challenge: understanding what the revised Federal Act on Data Protection requires and translating those obligations into workable business processes. The revised Swiss Federal Act on Data Protection, commonly referred to as the nFADP or revised FADP, has applied since 1 September...

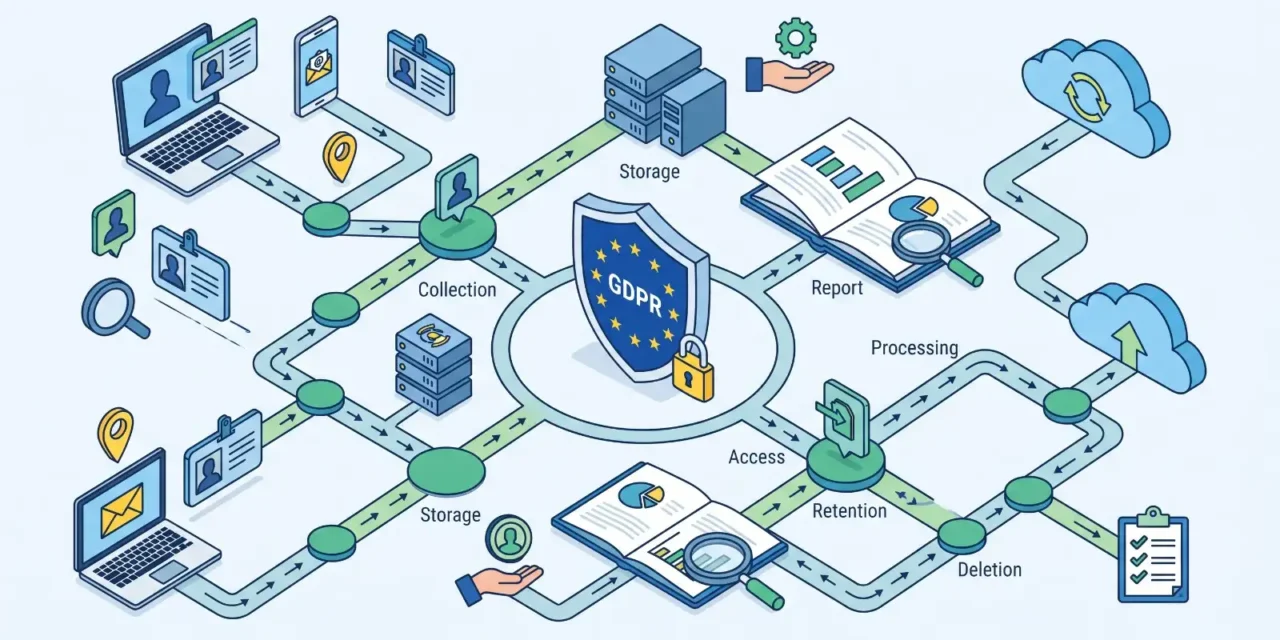
GDPR Data Mapping Services

What if your organization could not clearly explain where its personal data comes from, where it goes, who can access it, or when it should be deleted? For many businesses, the problem is not a lack of privacy policies. It is a lack of visibility. GDPR data mapping services help organizations build a clear picture...

Data Privacy Impact Assessment

What happens when a new technology, service, or business process creates significant privacy risks before anyone has formally assessed them? A Data Privacy Impact Assessment, commonly called a DPIA, is designed to answer that question before potentially high-risk processing begins. For organizations handling personal data, privacy should not be treated as a document created after...

Online tracking compliance – Navigating Complex Digital Realities

Consider this: on average, a single user’s online activity across Europe is broadcast to 376 companies every day, a staggering figure that underscores the pervasive nature of digital tracking and the monumental task of ensuring data privacy. This revelation, from a 2022 study by the Irish Council for Civil Liberties (ICCL), highlights the intricate web...

ePrivacy directive compliance – Navigating the Digital Frontier

Do you know that a staggering 80% of cookie consent pop-ups across Europe still exhibit ‘dark patterns’ that subtly manipulate users into accepting tracking, often in direct violation of the ePrivacy Directive? For data protection professionals, this statistic from a 2023 study by the Irish Council for Civil Liberties (ICCL) underscores a critical truth: achieving...

Page top